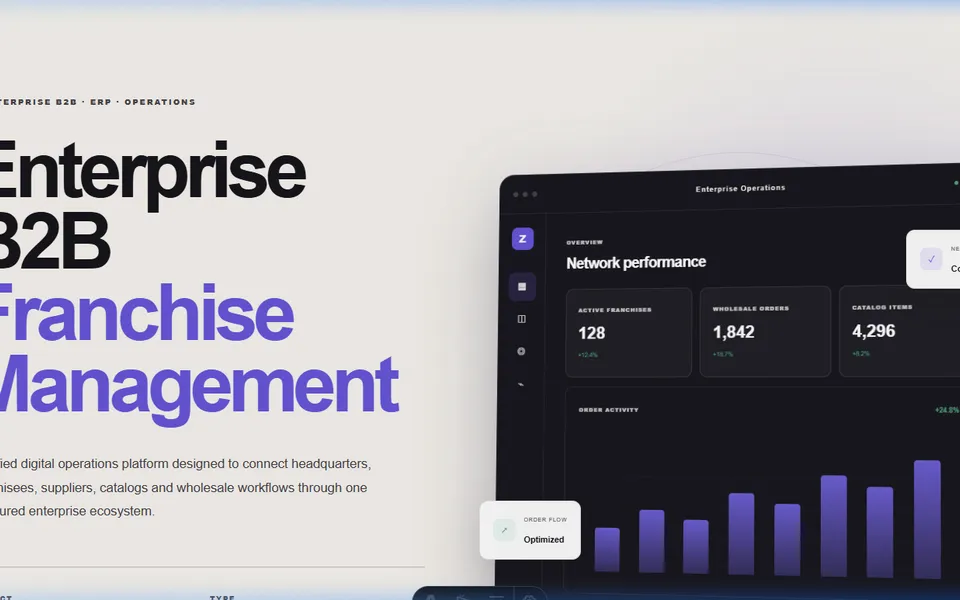
Enterprise Franchise Platform
Zero Downtime 500+ Branches
Neutralized multi-tenant privilege escalation and SQL injection flaws across 500+ franchise branches, guaranteeing zero downtime and complete data isolation.
English
Spanish
French

Polish
Italian
German
English
From PHP web shells to Node.js exploits, we isolate compromised servers, strip out malicious payloads, and patch security holes without disrupting your production workflow.
Automated malware scanners and hosting auto-reinstallers only treat symptoms. If the root code vulnerability is not patched, the backdoor re-infects your stack within 48 hours.
When an attacker compromises a server, they leave behind covert persistence mechanisms: obfuscated PHP scripts hidden inside legitimate upload directories, compromised npm dependencies triggering remote code execution, rogue cron jobs executing curl backdoors, and forged admin accounts in your database.
Zatnum's engineering unit combines static AST analysis, filesystem forensics, and live log auditing to surgically purge malicious artifacts while keeping your core application alive. We identify the exact entry flaw, write the surgical code patch, and wrap your environment in hardened WAF rules so you never face blacklisting or data theft again.
Rapid containment for active breaches and live malware outbreaks.
Surgical hot-patching keeps your customers purchasing uninterrupted.
Full snapshot rollback safety with zero database or customer record loss.
Root-cause incident documentation and blacklist de-listing support.
Surgical eradication and backend hardening across modern and legacy technology stacks.
Detection and elimination of obfuscated web shells (c99, r57, wso, eval-based injectors), vulnerable file-upload bypasses, unauthorized cron tasks, and tampered CMS core files. We audit server-side MIME verification and seal execution rights in media upload paths.
Neutralizing prototype pollution, malicious or vulnerable npm dependencies, insecure deserialization, and Remote Code Execution (RCE) vectors. We refactor insecure child_process/eval calls and enforce strict schema-based input sanitization.
Mitigating blind and union-based SQL injection (SQLi), JWT token forgery loops, unvalidated redirect chains, and unauthorized privilege escalation. We migrate queries to parameterized statements and re-sign authentication secrets.
Identifying hidden SSH authorized_keys, unauthorized sudo users, rogue systemd daemons, crypto-miner background tasks, and misconfigured Nginx or Apache reverse proxies allowing path traversal (..;/).
Targeted technical resolution for php2shell exploits, node2shell vulnerabilities, and critical CVEs.
Attackers exploit Windows and Apache mod_cgi argument escapes in PHP to execute arbitrary commands and deposit obfuscated c99, r57, and WSO web shells in writable upload folders.
Patching runtime binaries to PHP 8.1.29 / 8.2.20 / 8.3.8, rewriting FastCGI query dispatch rules, and sealing upload directories with deny all execution blocks.
Insecure deep-merge and recursive copy routines allow attackers to pollute Object.prototype, hijacking internal Node.js child_process templates to spawn unauthorized reverse shells.
Pinned lockfile audit, freezing Object.prototype via Object.freeze, and implementing Zod strict object validation schemas to reject prototype keys.
Flaws in sandbox libraries like vm2 allow untrusted code executed in host applications to break out of sandboxed contexts and trigger system-level child_process.exec() shells.
Migrating isolated code compilation to dedicated containerized microservices and V8 isolated contexts with strict syscall seccomp filters.
Buffer overflow flaws in phar and XML processing pipelines can be triggered by crafted file uploads, allowing attackers to hijack memory registers and execute shellcode.
Immediate upstream binary patch, disabling phar.readonly=On, and disabling high-risk functions (exec, system, passthru, proc_open) in php.ini.
Path traversal flaws in experimental permission model implementations allow malicious inputs to bypass --allow-fs-read and trigger unauthorized file modifications and script execution.
Upgrading Node.js to LTS 20.11.1 / 21.6.2, enforcing OS-level user namespaces, and revoking unnecessary file write capabilities for the application user.
Concealed web shells disguised as legitimate cache or thumbnail files (e.g. cache_temp.php, .php%00.jpg) utilizing dynamic string evaluation to execute commands and dump databases.
Full recursive AST filesystem hashing against clean upstream releases, quarantine of unauthorized files, and Cloudflare WAF OWASP Core Rule Set deployment.
Methodical execution, zero data loss, and bulletproof long-term security.
Immediate snapshot of server state, log preservation, and containment of active outbound command-and-control connections.
Deep recursive filesystem and database scan to strip out webshells, base64 payloads, and unauthorized modifications.
Patch the exact underlying vulnerability (input validation, dependency updates, sanitization, strict MIME checks) so reinfection is impossible.
Lock down file permissions, configure Web Application Firewalls (WAF), enforce strict headers (CSP, HSTS), and deploy integrity monitoring.
Speak directly with a senior backend security engineer. We will review your symptoms, assess exposure, and outline an emergency remediation plan.
Whether your website is actively blacklisted by Google, your hosting account is suspended, or you suspect unauthorized server activity, we will triage the situation on a live video bridge.
Explore how Zatnum isolates vulnerabilities, modernizes legacy code, and protects production systems.
Neutralized multi-tenant privilege escalation and SQL injection flaws across 500+ franchise branches, guaranteeing zero downtime and complete data isolation.
Eradicated legacy unauthenticated file-upload vectors, refactored media storage execution rights, and deployed Cloudflare Enterprise WAF to thwart scrapers.
Hardened Node.js microservices against prototype pollution and JWT replay attacks, structuring secure session validation and end-to-end API rate-limiting.
Everything you need to know about our web remediation protocols.